



**Dutch Cybercriminal Arrest Triggers Wave of Brazen Cyberattacks by ShinyHunters**
Authorities in the Netherlands have apprehended a 24-year-old convicted cybercriminal suspected of assisting the prolific hacker collective ShinyHunters with data thefts and extortion campaigns. In a dramatic turn of events following the arrest, remaining members of ShinyHunters escalated their operations significantly, launching a highly publicized breach at the Federal Bureau of Investigation (FBI) and extorting the notorious Russian ransomware group Cl0p.
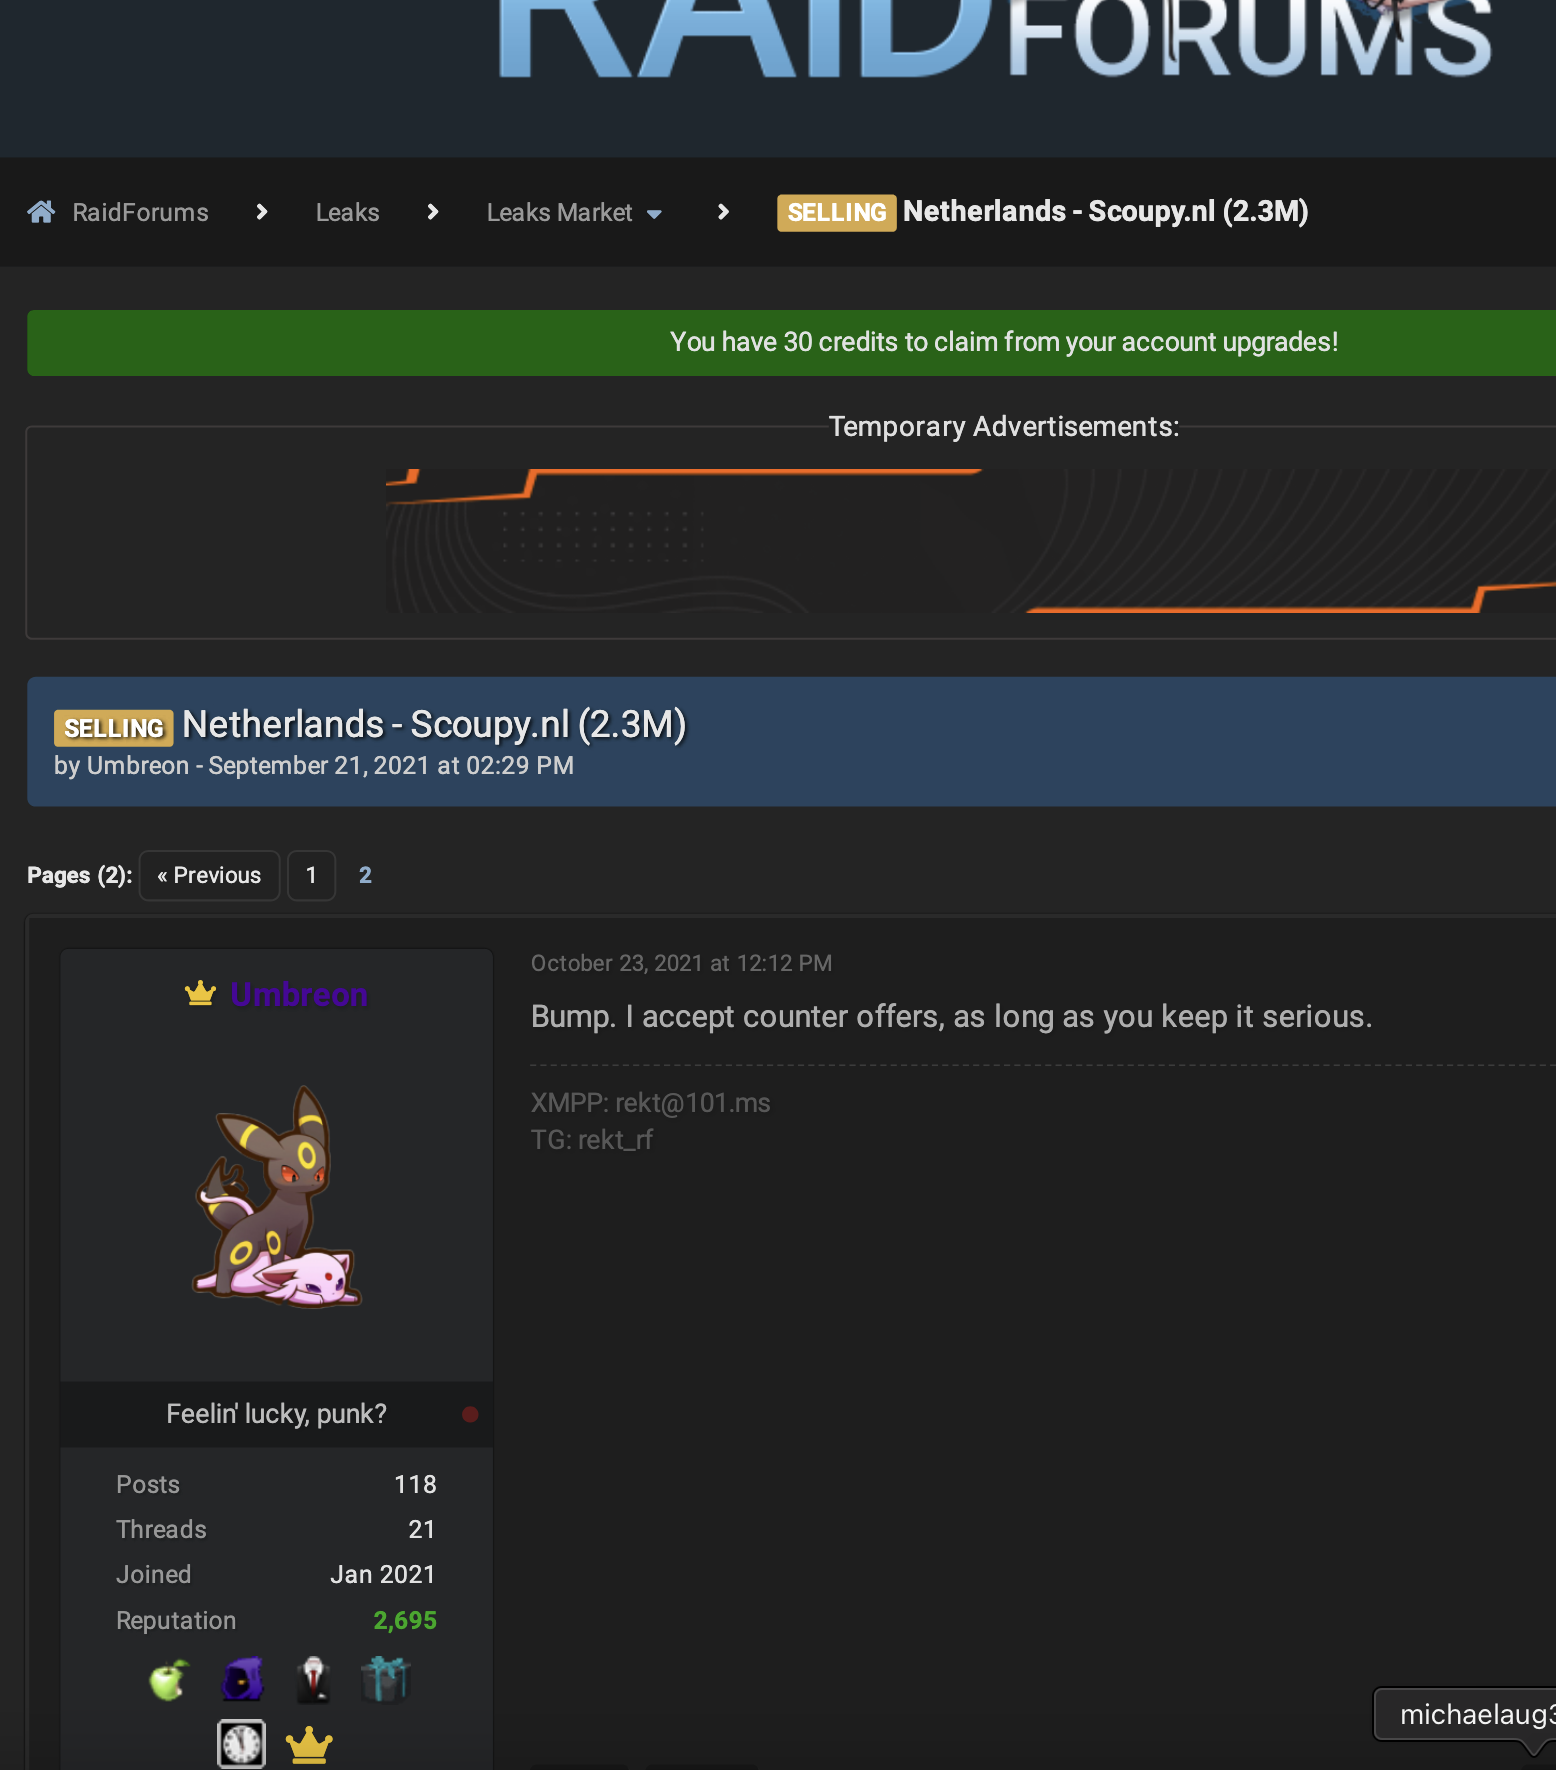
The individual taken into custody has been identified as Pepijn van der Stap, a resident of Almere and Lelystad who was previously convicted in 2023. Prosecutors stated that his earlier criminal activities generated between €1.5 million and €2.7 million through a series of data thefts and extortions. During his trial, van der Stap admitted to maintaining a double life, operating under the hacker alias “Umbreon” to steal and publish victim data on underground forums, all while working by day as a software engineer and volunteering at a Dutch nonprofit vulnerability disclosure group.
Van der Stap was sentenced to four years in prison, serving part of his time before his release in late 2025. He has since spoken publicly about seeking redemption, claiming to be a reformed individual aiming to contribute positively to society. However, his communications ceased abruptly in mid-September, shortly after authorities moved in. Reports indicate that Dutch police arrested van der Stap around September 16, and items were observed being removed from his residence.
The timing of the arrest appears to have triggered a shift in ShinyHunters’ strategy. The group claimed responsibility for a breach of the FBI’s public job application portal, exfiltrating Social Security numbers and personal data of over 5,000 officials, including sensitive psychiatric and medical records. The intrusion was traced back to the exploitation of a patched vulnerability in PeopleSoft, a widely used human resources platform owned by Oracle. ShinyHunters reportedly began exploiting this flaw as a zero-day in June and later refined their attack methods to bypass specific security mitigation rules designed to protect organizations that could not immediately patch the software.
Adding a personal touch to the FBI attack, the defacement page left by the hackers featured a large ASCII art rendition of the Pokemon character Umbreon—the very handle used by van der Stap. Investigators noted that this imagery mirrored a signature used by the group during an early attack on a cybercrime forum, raising questions about internal attribution within the collective.
Cybersecurity researchers have identified a recent power shift within ShinyHunters, attributing the group’s more erratic and aggressive behavior to a teenage hacker from Amman, Jordan, operating under the alias “Rey.” Rey is believed to be part of a merged cybercrime syndicate combining elements of Scattered Spider, LAPSUS$, and ShinyHunters. Sources suggest Rey had a contentious relationship with van der Stap over control of the group’s brand and stolen data. The oversized Umbreon image left on the FBI site is widely believed to have been a deliberate attempt by Rey to frame van der Stap for the intrusion.
In a separate incident, ShinyHunters also targeted Odido, the largest mobile telecommunications provider in the Netherlands, stealing data on over 6.2 million individuals in February. The group managed to social engineer an Odido employee into entering credentials on a spoofed website after a phone call conducted in native Dutch. While authorities have released a recording of the call and are asking the public for help identifying the voice, ShinyHunters confirmed the caller was a member and mocked local law enforcement, calling them incompetent and irrelevant.
The group’s recent spree also includes an extortion attempt against Cl0p, a highly respected Russian ransomware-as-a-service operation. This bold move, alongside the mass exploitation of the PeopleSoft vulnerability across multiple industries—ranging from healthcare and education to government—signals a new, high-risk era for ShinyHunters, which is projected to have earned close to $100 million in extortion payments this year alone.
***
**Frequently Asked Questions (FAQ)**
**Q1: Who is Pepijn van der Stap?**
A1: He is a 24-year-old Dutch cybercriminal previously convicted in 2023 for data theft and extortion that earned between €1.5 million and €2.7 million. He operated under the alias “Umbreon” and was a software engineer at a cybersecurity startup and a volunteer at a vulnerability disclosure nonprofit.
**Q2: What is ShinyHunters?**
A2: ShinyHunters is a prolific hacker group known for conducting large-scale data thefts and extortion campaigns against various organizations, ranging from government agencies to telecommunications providers.
**Q3: How did ShinyHunters breach the FBI?**
A3: The group exploited a patched vulnerability in PeopleSoft (CVE-2026-35273), a human resources software platform, which they initially targeted as a zero-day in June. They later used a URL-encoding technique to bypass security rules designed to stop them.
**Q4: Who is Rey, and what is his connection to ShinyHunters?**
A4: Rey is a teenage cybercriminal from Amman, Jordan, who has taken over the leadership of ShinyHunters as part of a merged group called ScatteredLapsussHunters (SLSH). Sources indicate he orchestrated the recent aggressive attacks and likely framed the former member van der Stap to assert control.
**Q5: What happened to Odido?**
A5: Odido, the largest mobile telecommunications provider in the Netherlands, suffered a data breach affecting over 6.2 million people. The attackers social engineered an employee over a phone call in February, tricking them into logging into a fake website to steal their credentials.
**Q6: Why did ShinyHunters attack the Russian ransomware group Cl0p?**
A6: As part of their recent escalation in brazenness, ShinyHunters targeted Cl0p for extortion, signaling a major shift from their previous operational tempo and a willingness to target even established cybercrime groups.
***
**Conclusion**
The arrest of Pepijn van der Stap has seemingly acted as a catalyst for ShinyHunters, propelling the group from a calculated data-theft operation into a phase of high-profile, retaliatory cyberattacks. With a teenager at the helm and a willingness to breach government databases and extort rival ransomware gangs, the threat landscape is evolving rapidly. The FBI breach and the Odido social engineering attack highlight the group’s technical capabilities and their readiness to exploit systemic vulnerabilities. As van der Stap remains in custody, the cybersecurity community watches closely to see how ShinyHunters will operate next and whether this internal power struggle will lead to further destabilization within the global cybercrime ecosystem.
Thank you for reading
