



# Canadian Cybersecurity Co-Founder Arrested in Connection with Major Hacking Investigation
Federal authorities in the United States have arrested a co-founder of a Canadian cybersecurity company in connection with an ongoing investigation tied to the ShinyHunters hacking group — a notorious cybercriminal organization responsible for stealing and extorting sensitive data from numerous high-profile targets, including U.S. federal law enforcement agencies.
## The Arrest
The arrest took place in Pennsylvania on October 8, when the suspect, identified as 54-year-old Edward Dubrovsky, was taken into custody on federal charges related to cyber extortion and conspiracy. Court documents filed in the Eastern District of Texas outline the charges, which include conspiracy to threaten the confidentiality of information with the intent to extort money and interference with commerce through threats.
Dubrovsky is currently being held at a federal facility in Philadelphia. Notably, court records indicate he does not yet have legal representation and has not been assigned a public defender.
## Who Is Edward Dubrovsky?
Edward Dubrovsky is a Canadian national who co-founded a cybersecurity company called Cypfer, which specialized in advising organizations on ransomware negotiations, extortion response, and settlement services. Cypfer was among the most prominent sponsors of a cybersecurity conference — the Cyber Risk Summit — held at the Loews Philadelphia Hotel from October 5 to October 7, just one day before Dubrovsky’s arrest.
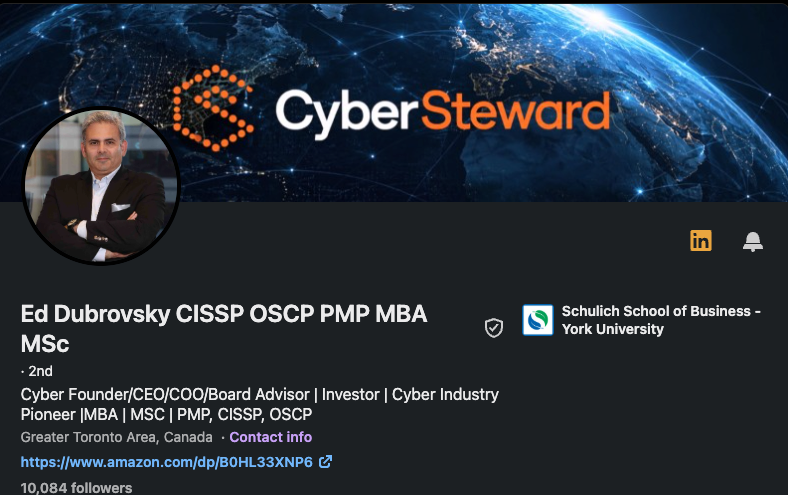
Dubrovsky’s LinkedIn profile indicates he later became associated with another Canadian firm called CyberSteward. In a post made roughly a month before his arrest, he expressed excitement about attending the Cyber Risk Summit with the CyberSteward team, writing about his work in “compliant-driven coercive advisory, negotiations and settlement services that are global and truly agnostic.”
Dubrovsky is also the author of a 252-page book titled *Cyber Extortion Strategic Response*, which explores the complexities of how organizations should respond to ransomware and extortion demands. The book emphasizes that engaging with criminals does not equate to agreeing to pay ransoms, and that communication can serve strategic purposes such as gathering intelligence and buying time.
## The ShinyHunters Connection
The ShinyHunters group has been responsible for a series of high-profile data breaches in recent months, targeting organizations through phishing attacks and stolen credentials. Once inside corporate systems, the group exfiltrates sensitive data and threatens to publish it publicly unless ransom payments are made. According to the FBI, the group has successfully extorted more than $70 million from victims so far this year.
A significant focus of the investigation centers on data stolen from the FBI’s own online recruitment portal, which exposed personal details of thousands of agents, including their unit assignments, specializations, and medical and psychiatric records. Following the breach, a member of the hacking group who goes by the alias “Rey” publicly taunted federal investigators.
Rey has since been identified as Saif Al-din Khader, a teenager who was detained by Jordanian authorities before being transferred to U.S. custody. Reports indicate that Khader is now cooperating with federal investigators.
## Broader Investigation Scope
The FBI’s ShinyHunters investigation has been centralized at a field office in Texas. In addition to Dubrovsky’s arrest, the investigation has been widened to include other companies that provide ransomware negotiation services. Key evidence in the case comes from devices seized last month when Dutch police arrested a convicted cybercriminal named Pepijn van der Stap in connection with the same investigation.
Sources familiar with the probe suggest that additional charges against individuals connected to ransomware negotiation services may be filed in the coming weeks.
—
## Frequently Asked Questions (FAQ)
**Q: What is the ShinyHunters hacking group?**
A: ShinyHunters is a cybercriminal organization known for infiltrating corporate systems, stealing sensitive data, and extorting victims by threatening to release that data publicly unless a ransom is paid.
**Q: What are the charges against Edward Dubrovsky?**
A: Dubrovsky faces federal charges including conspiracy to threaten the confidentiality of information with the intent to extort money and interference with commerce by threats.
**Q: What is Cypfer and what did it do?**
A: Cypfer is a Canadian cybersecurity company co-founded by Dubrovsky that offered advisory services on ransomware negotiations, extortion response, and settlement strategies for organizations affected by cyberattacks.
**Q: How much has ShinyHunters extorted from victims?**
A: According to the FBI, the ShinyHunters group has extorted more than $70 million from victims so far this year.
**Q: Who is “Rey” in the ShinyHunters investigation?**
A: “Rey” is the alias of Saif Al-din Khader, a teenager who was identified as a member of ShinyHunters. He was detained by Jordanian authorities and is now cooperating with the FBI.
**Q: Why was the case moved to the Eastern District of Texas?**
A: The case was transferred to the Eastern District of Texas shortly after Dubrovsky’s arrest, as that federal district has become the central hub for the FBI’s ShinyHunters investigation.
**Q: Has Dubrovsky been appointed a lawyer?**
A: As of the latest available court records, Dubrovsky does not currently have an attorney and has not yet been appointed a public defender.
—
## Conclusion
The arrest of Edward Dubrovsky marks a significant development in the FBI’s sweeping investigation into the ShinyHunters hacking group. As authorities continue to unravel the networks that support cybercriminal operations — from the hackers themselves to the firms that advise ransomware victims on negotiation strategies — the case raises important questions about the boundaries of cybersecurity advisory services. The investigation remains active, and further arrests or charges are anticipated in the weeks ahead.
Thank you for reading
