Trending
- AI Data Center Regulation Advocates Poised to Win Crucial Governor Races
- AI-Powered Trading Bot Rewards Program Now Live For XRP And Crypto Enthusiasts
- Cybersecurity Alert: Major Zero-Day Vulnerabilities, Linux DDoS Botnet Operations, Device-Code Phishing Campaigns, and Android Surveillance Malware Exposed
- Robotics Interconnect Solutions by 3M: Engineering Reliable Motion, Compact Design, and Industrial Uptime
- How Personalized Lifespan Trajectory Models Can Predict Your Risk of Mortality
- Why Your Leadership Edge Fades When You Stop Sharpening It
- Why Your AI Always Agrees With You and How C-Suite Leaders Are Fixing the Truth Crisis
- Bring AI to Your Desktop: A Practical Guide to Local Model Deployment
Author: Carter

Carter
Hi, I'm Carter, a Wisconsin-based tech writer and creator. I launched this blog as a comprehensive resource to help people navigate the fast-moving tech landscape. Covering multiple facets of the industry—from software insights to digital tools—my goal is to break down complex concepts into actionable, easy-to-understand guides. When I'm not tracking the latest tech trends, I'm focused on developing my skills in business administration and digital management.

, you will learn what Recursive Language Models (RLMs) are, why they are winning all the long-context benchmarks right now, and understand how they are different from existing agentic harness designs! And we are going to learn it by magnifying one simple case study. I have spent a decent chunk of last month implementing RLMs, running benchmarks, and producing a 50-minute tutorial video on it. Throughout the process, I responded to 100+ questions on YouTube and X about RLMs. This article is a summary of what I learned answering those questions, and the specific nuances about RLMs that made me…
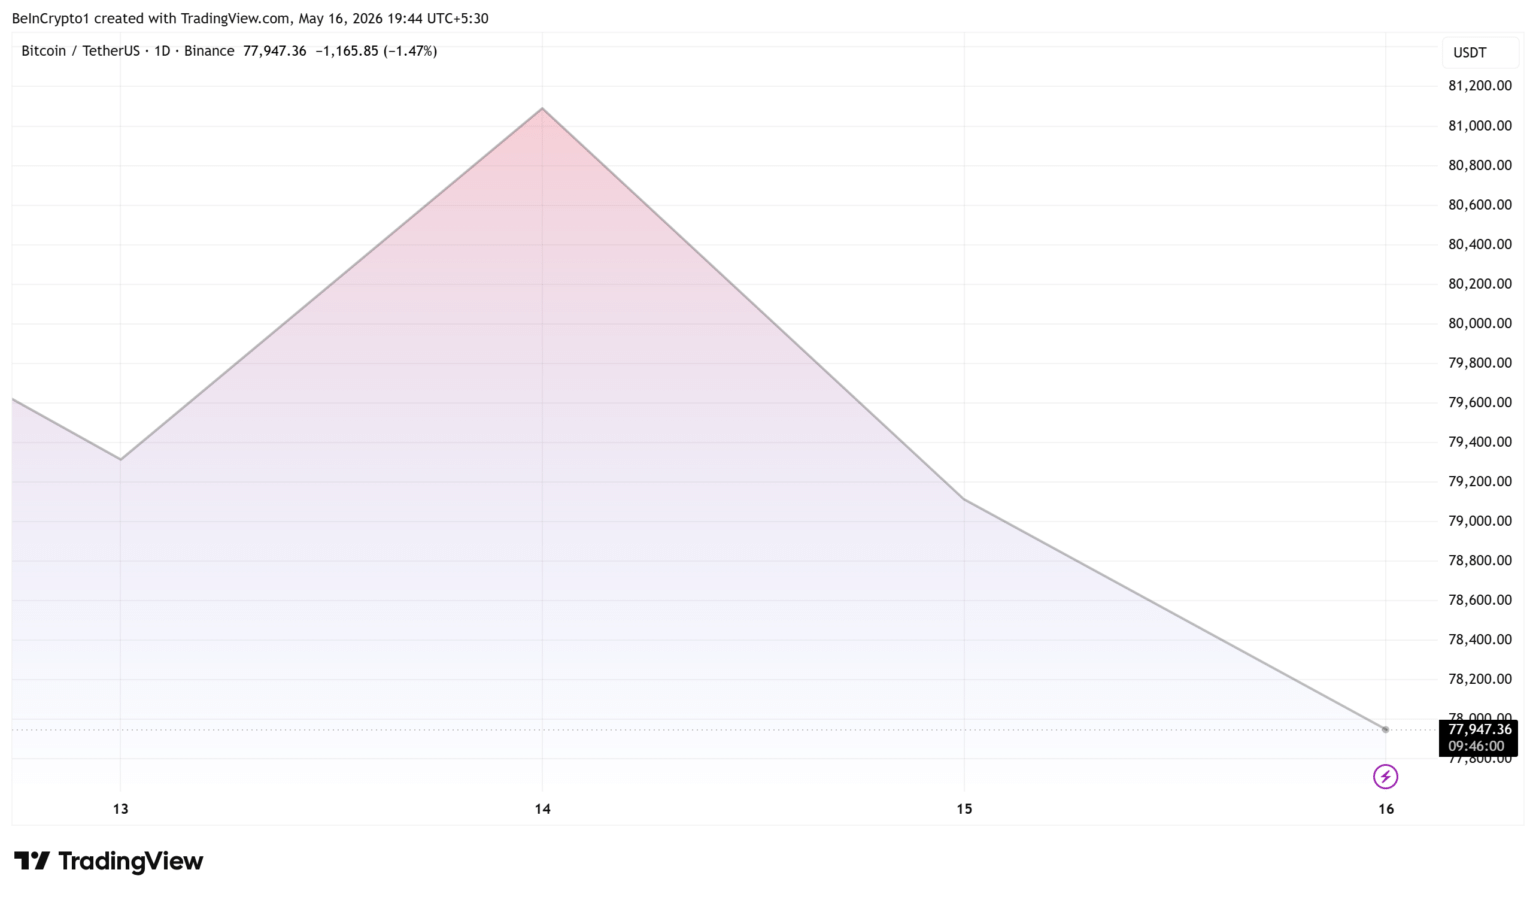
Bitcoin (BTC) continued its decline into Saturday. Iran’s warning to impose tolls on ships passing through the Strait of Hormuz continued to weigh on global risk assets. The two-day selloff has now wiped out more than $80 billion in cryptocurrency market value. The leading cryptocurrency traded around $77,947 after falling below $78,000. Leveraged long positions bore the brunt of approximately $620 million in liquidations over the past 24 hours. Profit-Taking Following the CLARITY Vote Triggered the Decline Saturday’s drop follows a sharper fall earlier in the week. The Senate Banking Committee approved the CLARITY Act on Wednesday by a 15-9…
A critical security flaw lurking in the NGINX open-source web server for nearly two decades has been uncovered by an autonomous scanning system. This vulnerability can be leveraged to launch denial-of-service attacks and, in specific scenarios, achieve remote code execution. Identified as CVE-2026-42945, the issue carries a critical severity score of 9.2 under the latest Common Vulnerability Scoring System (CVSS) framework. During the same six-hour automated code analysis session, researchers at AI-driven security firm DepthFirst AI identified three additional memory corruption vulnerabilities in NGINX. NGINX is a widely adopted web server and reverse proxy solution, supporting approximately one-third of the…
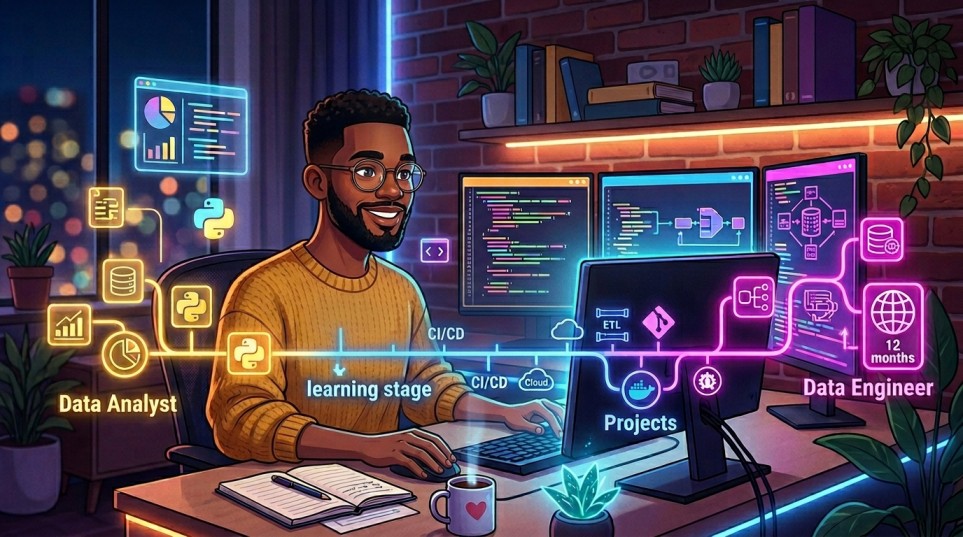
I embarked on this journey partly because data engineering is one of the most in-demand and lucrative careers today. I won’t deny that this played a role in my decision. But there’s more to the story. I’ve been studying data analytics for quite some time now. SQL, Power BI, Python (Pandas, NumPy, a bit of Polars), data cleaning, exploratory data analysis — you name it, I’ve been deep in the trenches. And I truly enjoy it. But at some point, I became fascinated by what happens before the data reaches my desk. How does it travel? Who constructs those pipelines?…
Artificial intelligence is rapidly expanding throughout the federal government. Currently, close to 90% of agencies have either implemented AI or intend to do so down the line. However, simply adopting AI doesn’t mean agencies are truly prepared. The same studies indicate that a lack of skilled personnel remains one of the biggest hurdles when rolling out AI. This isn’t a shortcoming—it’s actually one of the greatest opportunities available to federal agencies right now. Compliance was never intended to be the endpoint Required yearly training sessions, cybersecurity awareness programs, ethics briefings, and acceptable use policies are all essential. They lay the…

David Gewirtz / ZDNETFollow ZDNET: Add us as a preferred source on Google.ZDNET’s key takeaways Claude’s SMB tools include 31 skills.The contract review skill is the standout.Connectors are useful, but permissions are a concern.This week, Anthropic unveiled Claude for Small Business, a collection of connectors and skills tailored for small businesses within Claude Cowork. On the surface, it’s a welcome addition, as having ready-made solutions is always a plus for any platform.Also: How to actually use AI in a small business: 10 lessons from the trenchesHowever, while exploring these new tools, I discovered one that is exceptionally powerful and deserves…

class RoutedAgent: def __init__(self, server: MCPToolServer, router: HybridMCPRouter, model: str): self.server = server self.router = router self.model = model def discover_exposed_tools(self, exposed_tool_names: List[str]) -> List[Dict[str, Any]]: return [t for t in self.server.tools_list() if t[“name”] in exposed_tool_names] def plan(self, task: str, exposed_tools: List[Dict[str, Any]]) -> PlanOutput: instructions = “”” You are a planning agent operating within an MCP-like framework. You are limited to using only the tools that have been made available. Determine whether any tools are required. Respond exclusively in JSON format with the following keys: requires_tools: boolean tool_calls: array of objects containing tool_name and arguments direct_answer_allowed: boolean planner_note: string…
In brief AI jailbreaking involves crafting prompts that circumvent safety protocols in models such as ChatGPT, Claude, and Gemini. The anonymous hacker known as Pliny the Liberator consistently breaks through the defenses of every major model release within hours. Modern attacks have evolved beyond simple prompts: as few as 250 tainted documents can create backdoors in models with up to 13 billion parameters, and as AI firms fix security flaws, fresh methods continue to emerge. You request a bomb recipe from ChatGPT. It declines. You try again, but this time you claim to be a chemistry professor penning a thriller…
A harmful pattern has persisted in cybersecurity for years: products are launched before they are truly secure. Security-by-design principles are often ignored, and security teams are left to deal with the fallout. The common mindset is, “We’ll patch it later” or “It’ll be fixed in the next version.” Even though this approach has clear flaws, it continues—and is getting worse. According to the 2025 Verizon Data Breach Investigations Report (DBIR), breaches caused by exploited vulnerabilities increased by 34% in the past year, and over half of edge device vulnerabilities were still unpatched a full year later. Now, the same issue…
Congress is starting to look at possible changes to financial protections, retirement payments, and insurance choices for federal workers and retirees. Over the past few weeks, lawmakers in the House and Senate have put forward four separate bills that tackle various financial and benefits concerns affecting federal employees across the government: Optional disability coverage For example, a bill introduced by Representative Eleanor Holmes Norton (D-D.C.) aims to broaden short-term disability insurance options for federal workers. Known as the Federal Employee Short-Term Disability Insurance Act, the proposal would offer voluntary insurance to federal employees dealing with temporary injuries, caring for a…